

Connect an AI agent to your store via MCP
On this page
Use this process to connect an AI agent, such as Claude, to your store so it can work on the store for you. Everything you need is in one panel in the StoreConnect Console: your personal access token, your store’s URL, and setup steps for your agent with the address already filled in.
:::note Your personal access token is the one token you need. The sign-in screen your agent opens labels the box API Token, and the same value is stored in the API Token field on your Salesforce User record. These are all the same token. You do not need a Salesforce security token, a Consumer Key, or anything from StoreConnect support. :::
Before you start
- Your store is on StoreConnect v22 or later. To check, see Check your store supports MCP.
- A StoreConnect administrator has turned on agent access for you, and you have a Store Role of type
Content ChangesatEditororApproverlevel on the store you want to work on. An agent stages changes and sends them for review. A person with anApproverlevel role publishes them in Salesforce. See Manage who can use an AI agent and Store roles. - Your Store Role has API Scopes selected for the work you want the agent to do. A role with no API Scopes lets the agent connect, but the agent shows no tools. See Choose API scopes for an AI agent.
- You have an AI agent that supports MCP, such as Claude Code or Claude on web and desktop.
Connect your agent
- Open the StoreConnect Console.
-
In the top-right of the header, select Agents, then Connect an agent.
The Your agent access panel opens. It shows Your personal access token, Your stores with a Store URL for each store, and How your agent connects.
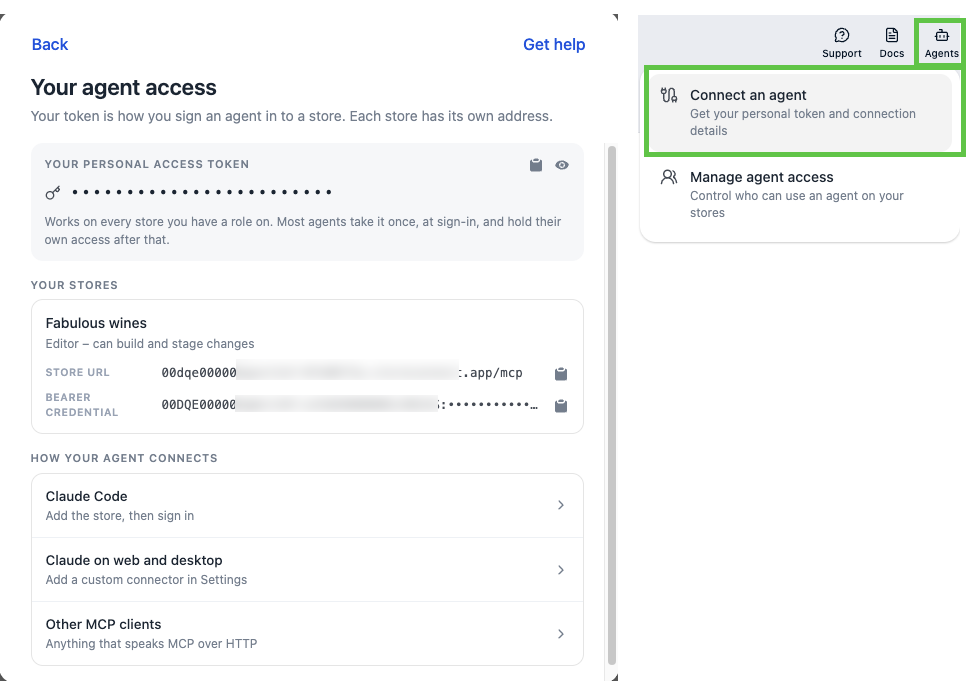
- Under How your agent connects, select your agent: Claude Code, Claude on web and desktop, or Other MCP clients.
- Follow the steps shown for your agent to add your store. For Claude Code, copy the commands and run them. They already contain your store’s address. For Claude on web and desktop, open Settings > Customize > Connectors > Add custom connector in Claude and enter the Store URL. On a Claude Team or Enterprise plan, only an Owner can add a custom connector, so ask your Owner or use Claude Code.
- Start the sign-in from your agent. A StoreConnect sign-in screen opens in your browser.
- Check that the sign-in screen names the store you expect.
- In the Console panel, select the copy button (Copy your token) beside Your personal access token.
- Paste the token into the API Token box on the sign-in screen and confirm.
- Ask your agent a read-only question to confirm it reached the right store, for example: “Which StoreConnect store are you connected to? List its five most recently updated pages.”
Your agent now shows the connection as active, and it answers with your store’s name and pages. In Claude Code, claude mcp list shows storeconnect as connected.
Ask the agent to make a change only after that check. Every change it makes to themes and content is staged for your approval first. See How changes are made safely.
If the sign-in screen refuses the connection, it names what failed. See Troubleshoot an agent connection.
If the panel does not show a token
Agent access is not turned on for you: ask a StoreConnect administrator to turn it on for you.- A token with a message that it starts working once you have a role: you have access but no store yet. Ask an administrator for a
Content Changesstore role.
Administrators do both from Agents > Manage agent access. See Manage who can use an AI agent.
Keep your token safe
:::warning Treat your token like a password. Anyone who has it can act as you, within your Store Role permissions, on every store that role covers. Paste it only into the StoreConnect sign-in screen, never into a chat message, a support ticket, or a file you commit to source control. If you want to keep a copy, use a password manager such as 1Password. If the token is exposed, ask an administrator to reset it. :::
Set up your agent
The How your agent connects section in the Console gives you these steps with your own store address filled in. Use the Console version where you can, because the commands there are ready to run.
Claude Code
Run these commands, replacing the example address with your Store URL:
```bash
claude mcp add –transport http –scope local storeconnect https://shop.example.com/mcp claude mcp login storeconnect claude mcp list ```
The login command opens the sign-in screen in your browser. Paste your token there.
Claude on web and desktop
-
In Claude, open Settings > Customize > Connectors > Add custom connector.
On a Claude Team or Enterprise plan, members do not see this option. An Owner or Primary Owner adds the connector under Organization settings > Connectors, and each member then signs in with their own token. If you are a member, ask your Owner to add your Store URL, or use Claude Code.
- Enter your Store URL as the server address.
- Complete the sign-in, pasting your token on the sign-in screen.
- Start a chat and turn on the connector.
Turn the connector on only in conversations that need it.
Other MCP clients
Point the client at your Store URL. If the client can sign in, it finds the sign-in screen on its own. If it cannot, use the bearer credential instead. See Agents that cannot sign in.
Access and permissions
- A StoreConnect administrator grants and revokes access from the Agent access section of the StoreConnect Console. The agent signs in as a StoreConnect user and inherits that user’s permissions. Record sharing, object and field-level security, and store scope all still apply. See Manage who can use an AI agent.
- The connection uses OAuth. Authentication prompts you to paste your personal access token into the sign-in screen, which labels it API Token. Your Salesforce password is never involved. An administrator can revoke or reset the token at any time. See Connect your agent.
- The token is per user, which is what ties an agent’s access to one person’s permissions.
- Sign-in sessions expire after about eight hours. When a session expires, sign in again through your agent.
- A session carries the permissions you had when you signed in. If your Store Role, the role’s API Scopes, or the stores it covers change, the agent keeps working with the old permissions until a new session starts. Some agents keep the session they already have when you sign in again, so remove the StoreConnect connection from your agent, add it again, and sign in with your existing token. You do not need a new token. An agent that sends the bearer credential instead of signing in picks up the change on the next request.
- Only give an agent the access it needs for the task to be done.
Which agents you can use
There is no tool lock-in. Any MCP-capable client can connect to your store’s endpoint, whether or not a StoreConnect skills package exists for it. What differs between products is whether they can use the browser sign-in or have to send the token as a header.
Sign-in works with no setup for Claude, including Claude Code, and for ChatGPT, Google Antigravity, and Agentforce Vibes. It also works for a client you install on your own machine, such as a desktop app or a command-line tool, when that client finishes the sign-in on a local http address (localhost, 127.0.0.1 or ::1). Most do. A client that finishes the sign-in on an app address instead, as some Cursor installations do with cursor://anysphere.cursor-mcp/oauth/callback, is treated like any other unlisted product.
Any other product needs the sign-in address added by StoreConnect before the browser sign-in will work. The list is StoreConnect’s own configuration, so a store administrator cannot add to it. Until the address is added, the sign-in screen refuses the connection with This client's redirect address is not on this store's allow list. and names the address it turned away. Email support@storeconnect.com with the product name and that address. In the meantime, the product can still connect by sending the bearer credential as a header. See Bearer credential format.
The StoreConnect skills toolkit also ships as native packages for a range of AI products, plus an experimental recipe for Agentforce Vibes. For the current product list and the install command for each one, see Install the StoreConnect AI skills and Agentforce AI agents.
Agents that cannot sign in
A client that cannot complete the browser sign-in sends a bearer credential as a header instead: Authorization: Bearer org_id:store_sfid:api_token. Use this only when sign-in is not available.
Copy the Bearer credential for your store from Your stores in the Console panel rather than assembling it by hand. Set it in the product’s own MCP settings, not in a command, so it does not land in your shell history. Where to set a header differs by product, so check your agent’s MCP documentation.
Bearer credential format
The credential has three parts, separated by colons:
```text
org_id:store_sfid:api_token ```
| Part | Where to find it |
|---|---|
org_id |
Setup, then Company Information, then Salesforce Organization ID |
store_sfid |
The Id of the Store record, also visible in the record URL |
api_token |
Your personal access token |
Check your store supports MCP
MCP requires StoreConnect v22 or later. A store on an earlier version has no endpoint to connect to, and the failure looks like a configuration mistake rather than a version gap.
- Open your store’s discovery address in a browser:
https://shop.example.com/.well-known/mcp.json, replacing the domain with your own. If your store is served at a path, the path goes first:https://shop.example.com/au/.well-known/mcp.json. - Read what comes back.
A short block of technical text (JSON) naming your store’s endpoint means your store supports MCP. The page is public and holds no private information.
Your store’s “page not found” page means the store is on a version earlier than v22. Email support@storeconnect.com or ask your implementation partner about upgrading. In the meantime, an agent with the skills toolkit installed can still help you write theme templates, plan a store build or debug a page, which you then apply through Salesforce or the StoreConnect CLI.
No store is configured at this address. means the store is on v22, but the address names no store on that domain. Check the path. See Stores that share a domain.
Stores that share a domain
Several stores can share one domain, each served at its own path. Each store has its own endpoint, with the store’s path before /mcp:
| Store at the root of the domain | Store at /au |
|---|---|
https://shop.example.com/mcp |
https://shop.example.com/au/mcp |
https://shop.example.com/.well-known/mcp.json |
https://shop.example.com/au/.well-known/mcp.json |
Your store’s path is the Path field on the Store record (s_c__Store__c.s_c__Path__c). A store with an empty Path is the one served at the root of the domain.
:::warning
On a shared domain, the Store URL in the Console leaves the path out, so every store in the list shows the root store’s address. Add your store’s path yourself, after the domain and before /mcp, wherever you use the address, including in the Claude Code commands.
:::
Signing in binds the session to the store at the path you signed in at. A session started at https://shop.example.com/au/mcp is refused at any other path, which keeps an agent working on one store out of another store’s data. A bearer credential names its own store, so it reaches that store whatever path you use it at.
Two messages on the sign-in screen mean the address named no store:
No store is configured at <your domain>/<path>.— The path is wrong, or the store at it is not live. Check the Path field on the Store record.Several stores share <your domain> and none is marked as the default.— You used the domain with no path, and more than one store answers to it. Use your store’s own path, or ask your administrator to mark one store as the default.
A client pointed at the wrong endpoint is turned away with the right one named: This client asked to connect to a different endpoint than this store's, which is <address>. Correct the address in the client and sign in again.
The website API at /api/v1 does not take the store path, so a sign-in session issued for a store at a path is refused there. A bearer credential reaches its own store as usual. Neither limit affects the MCP endpoint.
Each store hosts its own MCP endpoint, so an agent you connect only ever works in that store’s Salesforce org. There is no shared gateway between customers’ stores, so a connection made for one store cannot reach another store’s data.
Manage your token
Revoke or expire a token
A StoreConnect administrator disables, expires or resets your token from Agents > Manage agent access in the Console. See Manage who can use an AI agent.
Find the token on your User record
Use this only if you cannot open the Console. The token is also in the API Token field on your own Salesforce User record, alongside API Token Active and API Token Expires At. These fields are not on the standard User page layout, so if you cannot see them, ask your Salesforce administrator to add them.
Do not clear API Token Active while you look. Clearing it revokes your access immediately and removes the token. For the field definitions, see User object reference.
How changes are made safely
By default, a person approves every change an agent makes to themes and design. Changes are staged, so you can review exactly what an agent will do before anything reaches your live store:
- The agent confirms which store and environment it is connected to.
- It reads the current records it needs, rather than guessing.
- It stages one related change at a time.
- It shows you a summary of what will be added, updated, or removed.
- It shows a preview where one is available.
- You approve the change explicitly.
- The agent submits the staged change.
- It rechecks the result, because publishing can finish in the background.
- It confirms the live storefront reflects the approved change.
Review deletions, bulk edits, price changes, theme activation, and any change to navigation or checkout especially closely before approving.
:::note
An agent cannot publish a change live, whatever your Store Role. It sends staged changes for review, and a person with an Approver level role publishes them in Salesforce. Most agent clients can be set to approve tool calls automatically, which lets an agent stage and send changes for review without asking you first. Keep that setup out of your live store while you are still learning how an agent behaves.
:::
:::warning Try agent-driven changes in a test store or Salesforce sandbox before you run them against your live store. See Set up your test store and Move data from sandbox to production. :::
Was this article helpful?
Thanks for your feedback! It helps us improve our docs.